introduction
nightmare eclipse, chaotic eclipse, dead eclipse, msnightmare. he's been through a few names these past few months
he's been casually dropping windows exploits since april, starting with bluehammer. most target defender or something around it
other researchers were posting about their own problems with msrc too. reports ignored, downgraded, or patched without a reply
i'd only followed it through the articles until he opened a discord server last evening
what everyone knew
it started on march 26th 2026 with a blog post:
But someone violated our agreement and left me homeless with nothing. They knew this will happen and they still stabbed me in the back anyways, this is their decision not mine.
then a week later he dropped bluehammer
he didnt say what the agreement was. in may he was still talking about unpaid reports:
You defame me in public with your CVE-2026-45585 advisory even though you literally deleted the Microsoft account I used to report bugs to you with and I got zero pennies from doing so.
the coverage i read treated it as a bug bounty dispute
microsoft answered on may 28th with an msrc post - "A shared responsibility: Protecting customers through Coordinated Vulnerability Disclosure". the vulnerabilities werent responsibly disclosed, customers were being put at risk, and they brought up the digital crimes unit and were working with law enforcement. they faced so much backslash that within days they put out a softer version: no intention of pursuing people doing or publishing security research, plus an admission that some of their interactions with researchers had fallen short
discord server
on august 18th, around 8:42 pm cest, the twitter account everyone attributes to him posted an invite
so i joined. there were bit more than 200 members, few text channels, one of them being called questions-that-may-or-may-not-be-answered (which aged well)
i kept running DiscordChatExporter over the channels every so often, because i felt like this server won't last
the microsoft story
at 9:32 pm he opened a thread. first message: "The Microsoft story"
someone asked how he even talks to microsoft. email, something encrypted?


i'd been reading about him as an external researcher. this was the first time i'd seen him say he worked at msrc
getting fired
 1
 1
this was october 2024, which somebody in the channel noticed straight away:

so about eighteen months between that meeting and the first exploit going out
the severance offers
 8
 2
 2
 1
 4
he also said he was up for a promotion, and that his own manager only found out the day before
the accusation
he begged gallagher for another meeting just to find out the reason for his firing. he got one:
 4
access
i asked if the two weeks couldve been his notice period, if he was still in probezeit
then he gave the dates:
 1
 1
 1
 1
 1
 1
 1
 1
 1
 1
 1
so the actual termination came months after the meeting. that doesnt explain the two weeks of access
court
he says people around him pushed him to sue. the hearing was may 2025
this was microsoft's defence:
1
 1
the additional sheet is where the work permission lives. so he brought that:
 1
1
 1
 1
the threat claim
then microsoft argued he'd threatened them, with a witness:
he put the end of the case a month before bluehammer, though the dates dont line up:
my questions
i asked whether he'd been fired without notice, and whether he'd asked for the reason in writing:

if you request it, the employer has to give you the reason in writing. did you ever request that from microsoft, what did they say?
the channel kept getting locked and unlocked so i dm'd him too, about whether he ever tried a neutral third party (cert/cc or similar) before any of this went public:
i (unfortunately) also live in germany, so i was wondering, was that a fristlose kündigung? asking because under §626(2) BGB, if you request it, the employer has to give you the reason in writing. did you ever request that from microsoft, what did they say?
i wonder if he ever ever try bringing in a third-party mediator/coordinator like cert/cc to try and resolve w/ ms before going public
i also asked if microsoft ever named the third party in court:
someone asked whether the court documents are public. "not yet"
not the bounty
at 11:05 pm cest i asked whether microsoft ever produced any evidence for the leak claim:
so why had he kept the firing quiet?
he didnt answer. a couple minutes later the server disappeared from my sidebar. on twitter shortly after: "Closed, too much headache"
fact checking
i saved the chat, but i dont have his court documents or a way to check who was behind the account
employment history
the verge and krebs had already reported that he might be an ex employee. the register asked microsoft about it on may 28th and got no answer
i kept seeing september 2022 to june 2025 given as his employment dates, usually citing krebs or the register. i checked both and couldnt find those dates in either. some write ups mentioned linkedin and hackerone too, but i couldnt trace it back
gallagher’s role
he calls tom gallagher his CISO. gallagher is vp of engineering at msrc. somebody in the channel checked his linkedin:

the dates
he said "that March last year", then put bluehammer a month later. bluehammer was april 2026. did he mean march this year?
microsoft's lawyer told him he'd only been there six months, he says three years. both can be true. the visa sheet names "Microsoft Deutschland GMBH" specifically. so if he moved onto the german payroll partway through, that job would only be six months old, while microsoft as a whole is still three (?)
what he admitted
and then theres this, fourteen minutes before he started the story:
 1
 1

i would like to see those court documents
what i think
maybe he is a bit of a hero for getting other researchers to speak up. people were talking about reports msrc had ignored or downgraded, and i think thats a good thing even if his own reason for doing this was different
but i cant really support releasing exploits people can use against others. huntress saw three of his exploits used against a company in april. none appears to have worked in that case
i still want to know why he kept the firing quiet for five months. i hope things start going better for him, but theres a lot here i cant check
update
august 19th
7:30 pm. i was finishing this article when he posted something on twitter suggesting that he had taken an overdose
august 20th and 21st
he kept posting:
september 11th
he's posting as "Abdelhamid Naceri" now:
his work history
theres a linkedin profile under that name with the september 2022 to june 2025 dates i couldnt find earlier:
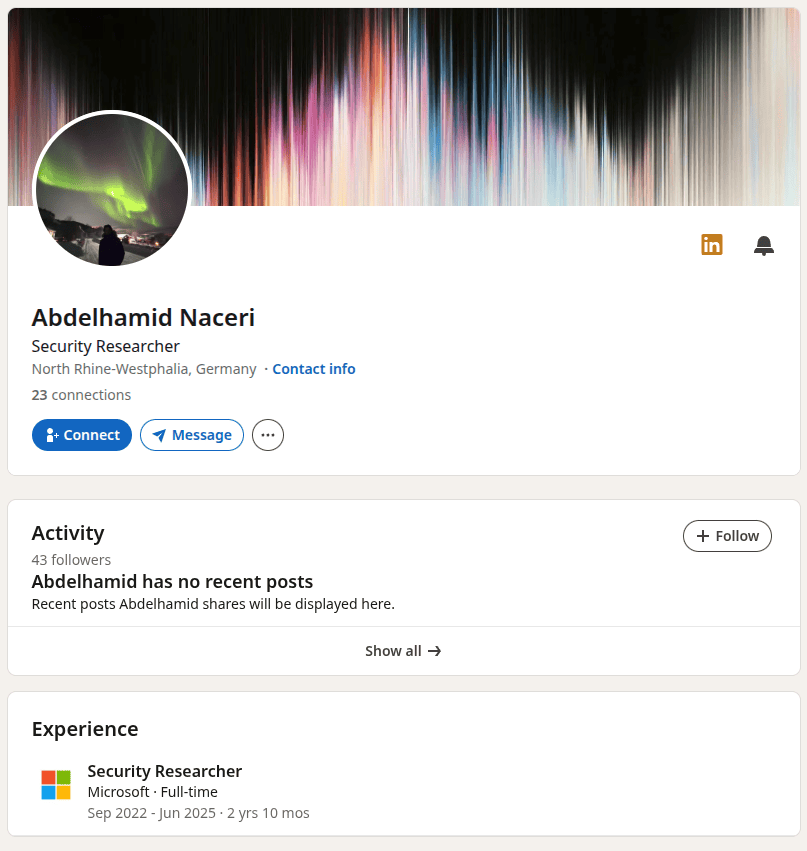
searching the name and the usernames halov and halove23 also turns up a long history of vulnerability research and cve credits. zdi credits "Abdelhamid Naceri (halov)" for CVE-2021-27070 and CVE-2021-45231, among others. halove23 also appears in an older mozilla vulnerability report
september 13th
he posted his side on twitter too, including an email from gallagher
the offers and email
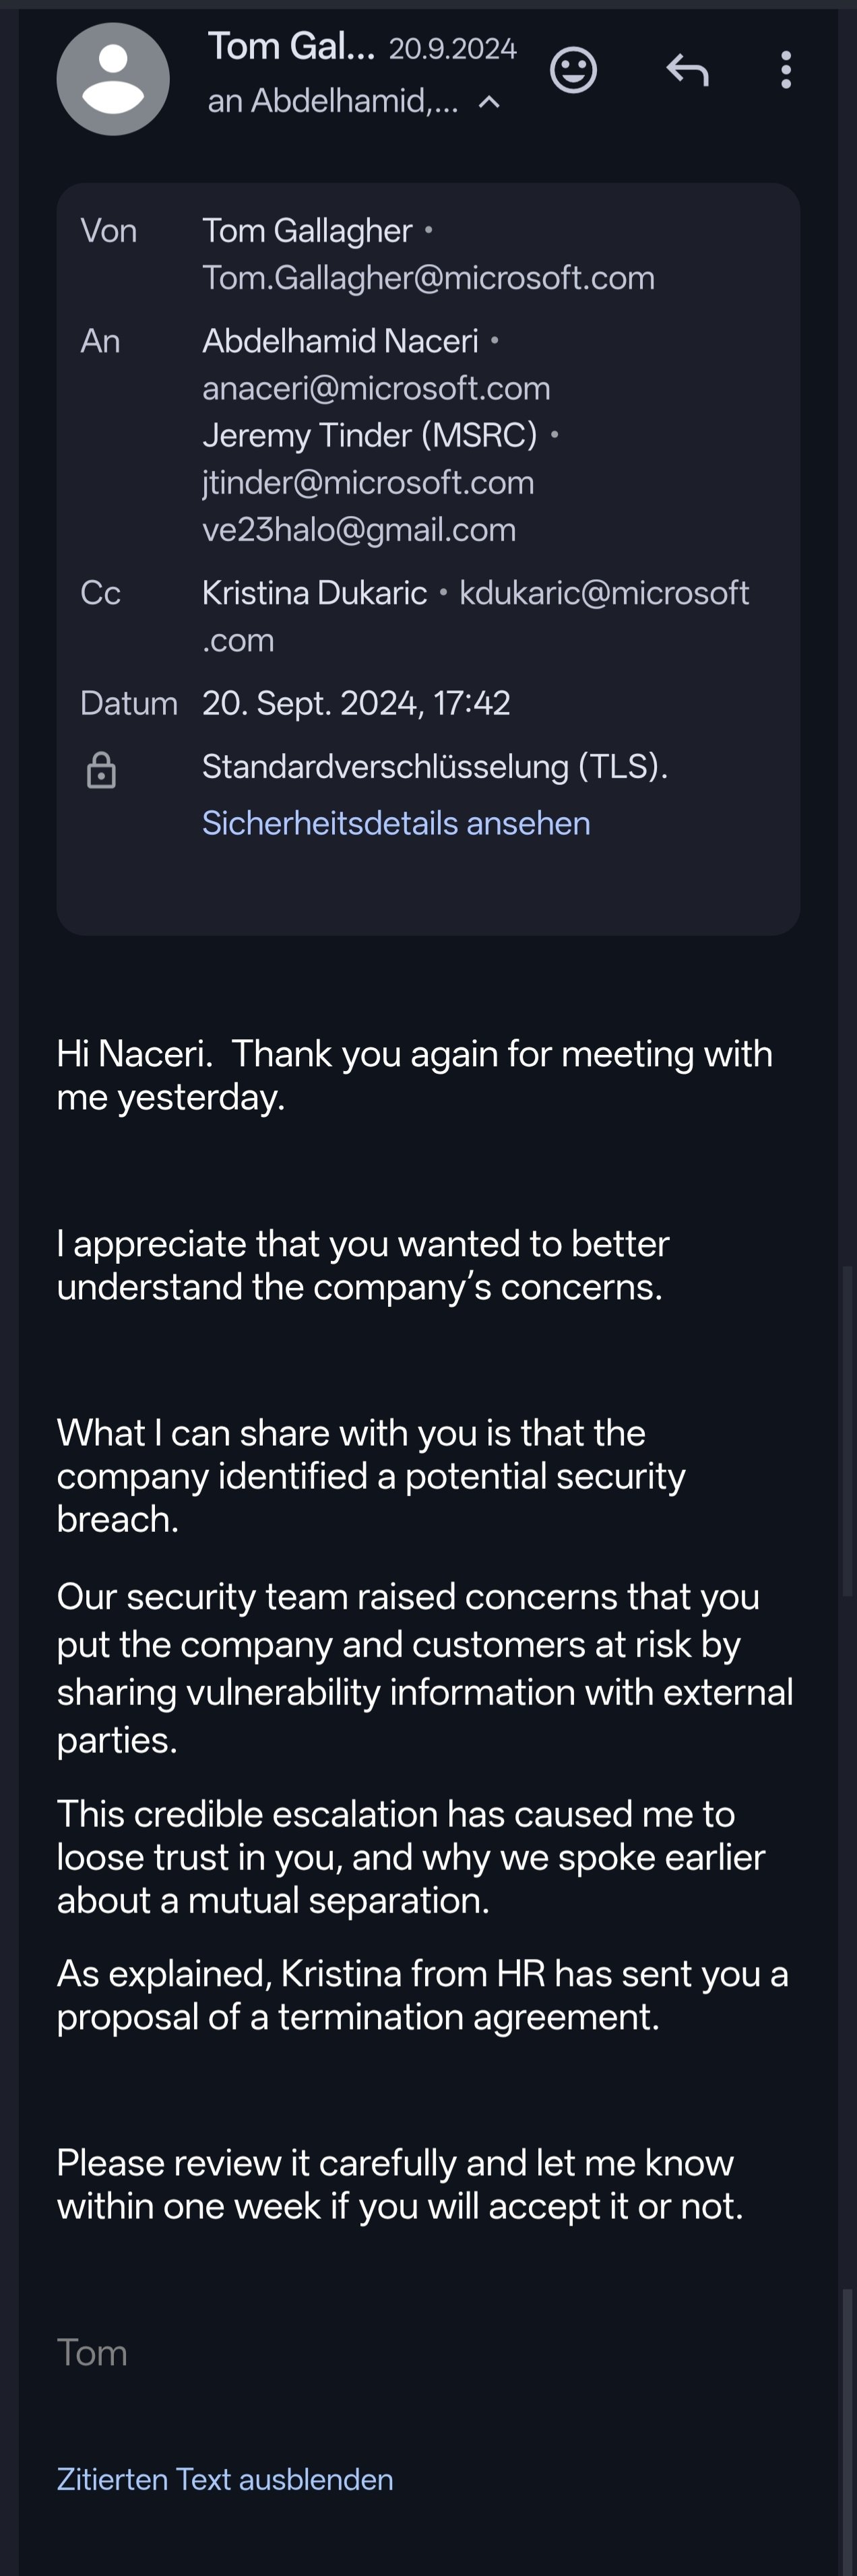
mostly the same story he told us in august. the meeting is now september 2024 instead of october, which fits the date on the email
termination and court
he also shared his termination letter, dated march 3rd 2025, with employment ending on june 30th. those dates match his earlier messages. it says he was released from work with continued pay (im not attaching the photo because it includes his home address)
he now says his visa had expired, after telling us all his documents were valid. not sure what to make of that
the aftermath
and then he added this:
comments
0 comments